Moving DNS hosting (for example to Cloudflare) is a common cause of broken email and “site down for some people” reports. Most failures come from records that were never copied. This checklist keeps the order safe.
1. Record everything before you touch anything
Run the domain through the DNS lookup and save A, AAAA, CNAME, MX, TXT, NS and any SRV records. If your current provider offers a zone file export, take that too. A standard lookup only resolves hostnames you explicitly ask for, so run a subdomain finder search to map out public and legacy hostnames (such as mail, autodiscover, app, and stage) that must be re-created at the new host. Also check your provider’s panel for DKIM selector records like selector1._domainkey and _dmarc.
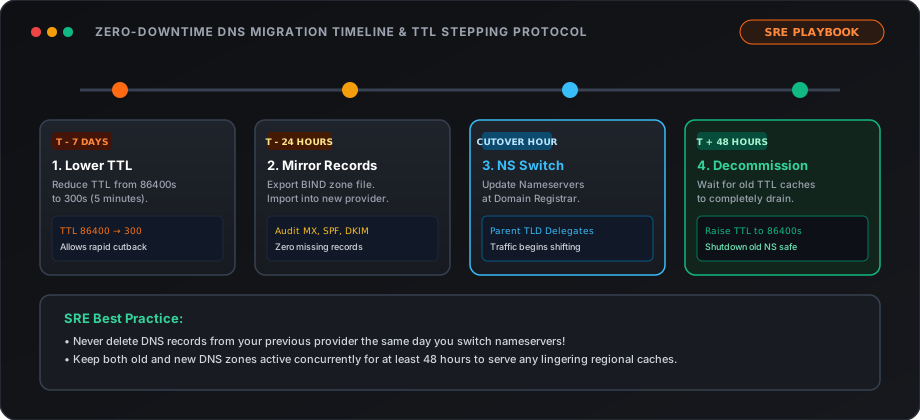
2. Lower the TTL a day ahead
Set the TTL on the records you will change to a low value (300 seconds is common) at least one full old-TTL period before the move. This shortens the time resolvers keep the old answers.
3. Recreate every record at the new provider
Copy MX, SPF (TXT starting v=spf1), DKIM and DMARC exactly. Typical misses: the DKIM selector, a second TXT verification record, and mail-related CNAMEs. Keep MX priorities the same. If you use a proxy feature at the new provider, leave mail records (MX targets and the hostnames they point to) as DNS-only.
4. Compare old and new before switching
Query the new provider’s nameservers directly and compare to your saved list. Check MX and DMARC specifically, because those are the records whose absence silently sends mail to spam or bounces it.
5. Change the nameservers at the registrar
Replace the NS records at your registrar with the two or more nameservers the new provider gave you. Do not delete the old zone yet.
6. Watch propagation, then verify
Use the propagation checker to see the NS change spread across public resolvers. It can take up to the old NS TTL, and registries may cache NS records longer than other records. Then re-run the site, SSL certificate and mail checks, and send a test message to a different mail provider.
7. Clean up
After a few days of stable results, remove the old zone, raise TTLs back to normal, and note the migration date so the next person knows where DNS lives.
Common mistakes
- Switching nameservers before copying the DKIM or MX records.
- Leaving two SPF records instead of merging them into one.
- Proxying a hostname that mail clients connect to directly.
- Deleting the old zone while resolvers still hold the old NS.
Running these checks gives you a snapshot, not a guarantee: caches differ by network, so confirm from more than one location if a user still reports a problem.
Stay Ahead on Protocol Changes
Get our authoritative engineering deep dives on Gmail/Yahoo bulk sender rules, post-quantum TLS, and DNS standards directly in your inbox. No marketing fluff.
Maximum 1 email per week · Unsubscribe with 1 click
Related tools
View all toolsDNSSEC Validator
Free DNSSEC validator. Verify the cryptographic chain of trust from ICANN root down to zone apex. Inspect DS records, DNSKEY public keys, and RRSIG validity.
DNS Time Machine
Free DNS Time Machine. Track DNS record changes with git-style visual diffs (+/-) and export standard RFC 1035 BIND zone files for 1-click disaster recovery.
DNS Propagation
Free global DNS propagation checker. Test A, AAAA, CNAME, MX, and TXT records across 12 worldwide edge locations with expected value matching and Geo-DNS detection.